The Entity Church Registry
A registry provides name resolution similar to DNS: given a name, which peer is it, and where do I reach it. It resolves a name to a peer identity, the endpoints that peer can be dialled at, the evidence for the association, and how long the answer is good for.
That is the whole job. Everything else — fetching a tree, verifying content, rendering a page — happens below it and does not involve the registry at all.
Concretely, an entry in this registry is six fields:
name:           "billslab.com"
kind:           "peer-issued"                 signed by the registry, not asserted locally
target_peer_id: "2KBj64an1PvKXMafcT2rCC8eaac4Kmyht7xTeCap8USWho"
transports:     [ <hash> ]                    → how to reach that peer
issued_at / ttl:                              an instant, and a duration — thirty days
Two hundred and nine bytes, signed, and it says who rather than where: the transports
hash points at a separate profile carrying the actual URLs. That indirection is most of
what people find surprising, and it is worth two minutes —
the same name, resolved end to end, with the real artifacts.
The shape of that walk, before the artifacts:
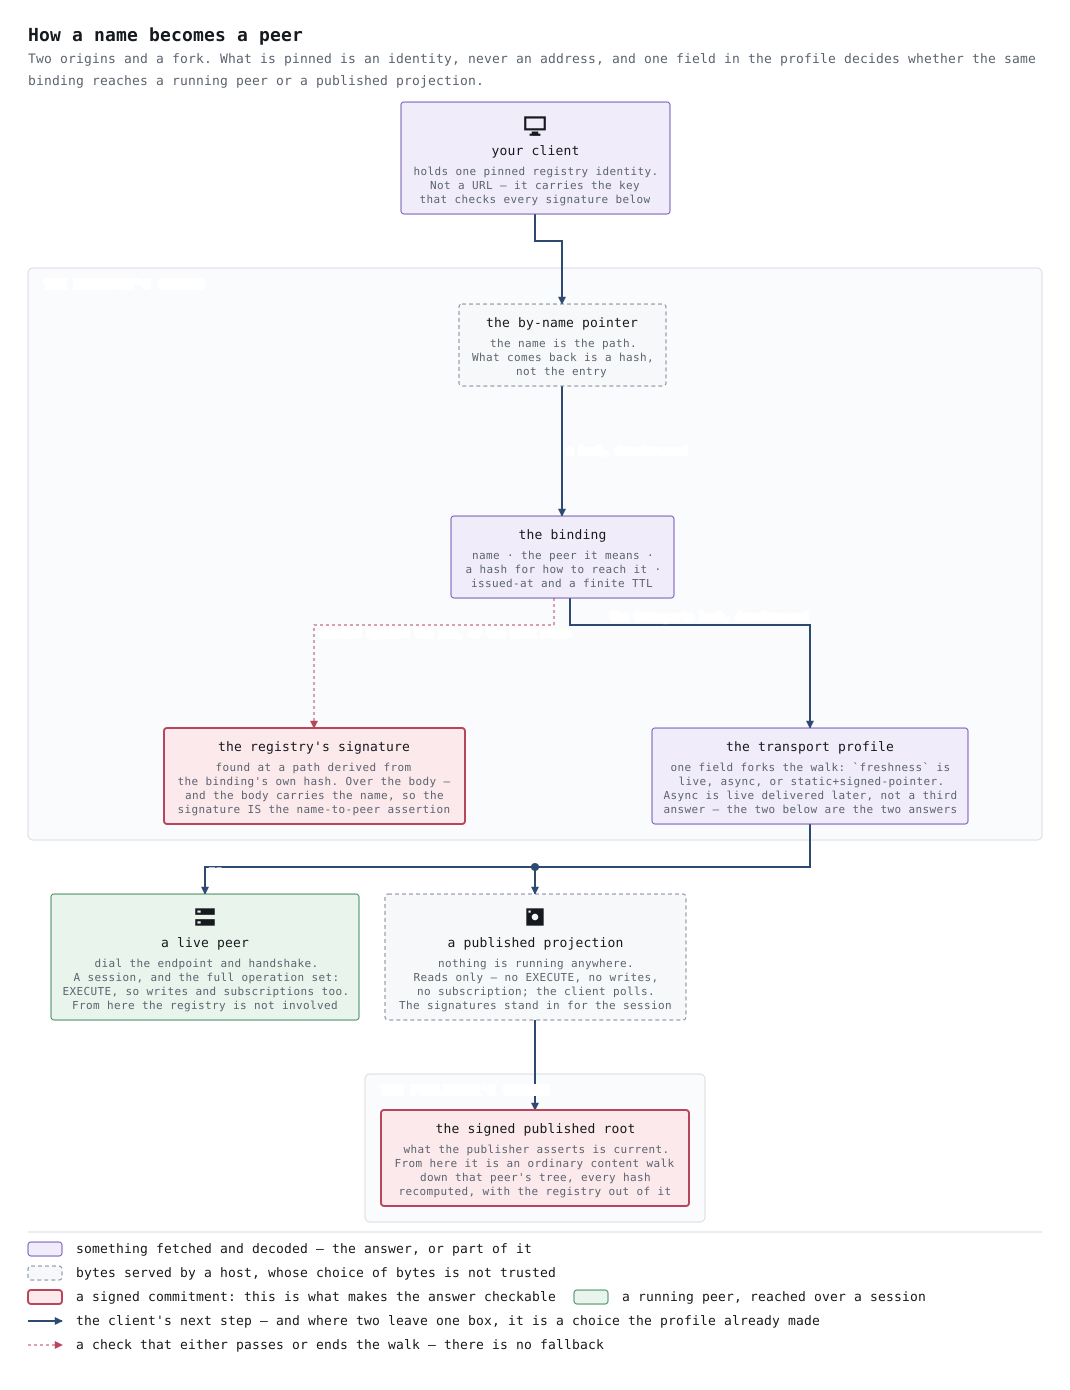
Two things in it are worth noticing before you read further. The second hop happens at a different origin — the registry hands over an address and is not involved in fetching anything. And the one line that is not a fetch is the check against your pin: it either passes or the walk ends. There is no path on that diagram where a failed check becomes a slightly-less-trusted answer.
What this registry is for
This is a working deployment run to exercise the design. The sites around it are a demonstration: several domains, published by different keys, resolving through this registry and linking to one another. There are more domains here than the content strictly needs, and that is deliberate — a name-resolution layer that is only ever described stays plausible, while one that has to actually resolve across independent publishers, from a real host, in a real browser, produces the failures worth knowing about.
So the honest description of this registry is: a small, real registry, running so that the design has somewhere to be explored. It carries the names this deployment needs. It is not an index of the network and makes no claim to completeness.
Concretely, it is static. The bindings are files — signed, published, and served by an ordinary host. There is no peer standing by to take a request: no sign-up, no submission form, nobody to ask. A name gets added when someone edits the deployment and republishes it. That is not a placeholder for missing infrastructure; a static registry is a supported shape, and it is the cheapest one that still proves the mechanism.
Whether it stays that way is open. A registry that accepts live registration, a sandbox that takes anything first-come-first-served, a curated one with a review step — all of these are reasonable things to build on this substrate, and they differ by trust model rather than by size. This one may grow into something people rely on. It is also fine if it doesn't, and the design should not care either way.
Preloaded is not default
You most likely did not choose this registry. It is the one shipped with these builds — preloaded, so that a fresh client can resolve something at all rather than starting from an empty configuration and a blank prompt.
The specification models this directly, and names the discipline that goes with it: distributions ship an opinion, and the user owns the configuration. The analogy it draws is the root certificates that come with an operating system — pre-trusted because you accepted the build, removable at any time. Pre-trust by acceptance is a real thing to have accepted, which is why it is worth stating on the front page rather than in a footnote:
- It is not required. Nothing about the protocol depends on this registry existing.
- It is not the default in any protocol sense. There is no default registry; a pin is explicit and unpinned resolution fails closed. What "preloaded" means is that this build made a choice on your behalf and told you so.
- Override is structural, not a favour. Point your configuration at a different registry, run several, order them how you like, or replace the shipped bindings with your own. The mechanism is exposed for exactly this.
What a name is worth here
There is no global namespace, and this registry does not create one. A name has no meaning on its own. It means what your resolver configuration says it means, and the same string can resolve to different peers for two people running different configurations. Anyone may publish a binding claiming any name; whether you trust that binding is your policy, not the registry's.
Three things follow:
- "Trusted" describes the path you resolved through, not the name. A name is trusted for you because your configuration pinned a registry whose signature you verify. To someone else the same name may be unknown, or resolve somewhere else.
- Uniqueness is per-receiver. Two registries may bind the same name to different peers. Your own priority order breaks the tie, and genuine ambiguity fails closed.
- This is DNS-shaped without a single root. There are delegated authorities, records and expiry times, but the root is whatever you chose to keep. Broad agreement about a name is something that emerges when many people trust the same registry. It is not built in, and it is not conferred by a domain.
Read on
- How a name resolves — one name taken end to end with the real artifacts: the entry, the transport profile it points at, the fetches, and what your client checks before believing any of it. Start here if you want to see the thing rather than read about it.
- Run your own registry — the shape of it, and why the interesting deployment is yours rather than this one.
- Browsing the registry — what a list of names is worth before it has been resolved, and what a browsing surface has to guarantee.
The normative reference is the registry extension and the resolution guide, both published with the rest of the architecture corpus at entitychurchfoundation.org. This site explains; those specify, and they win on any conflict.